Who did what, and when
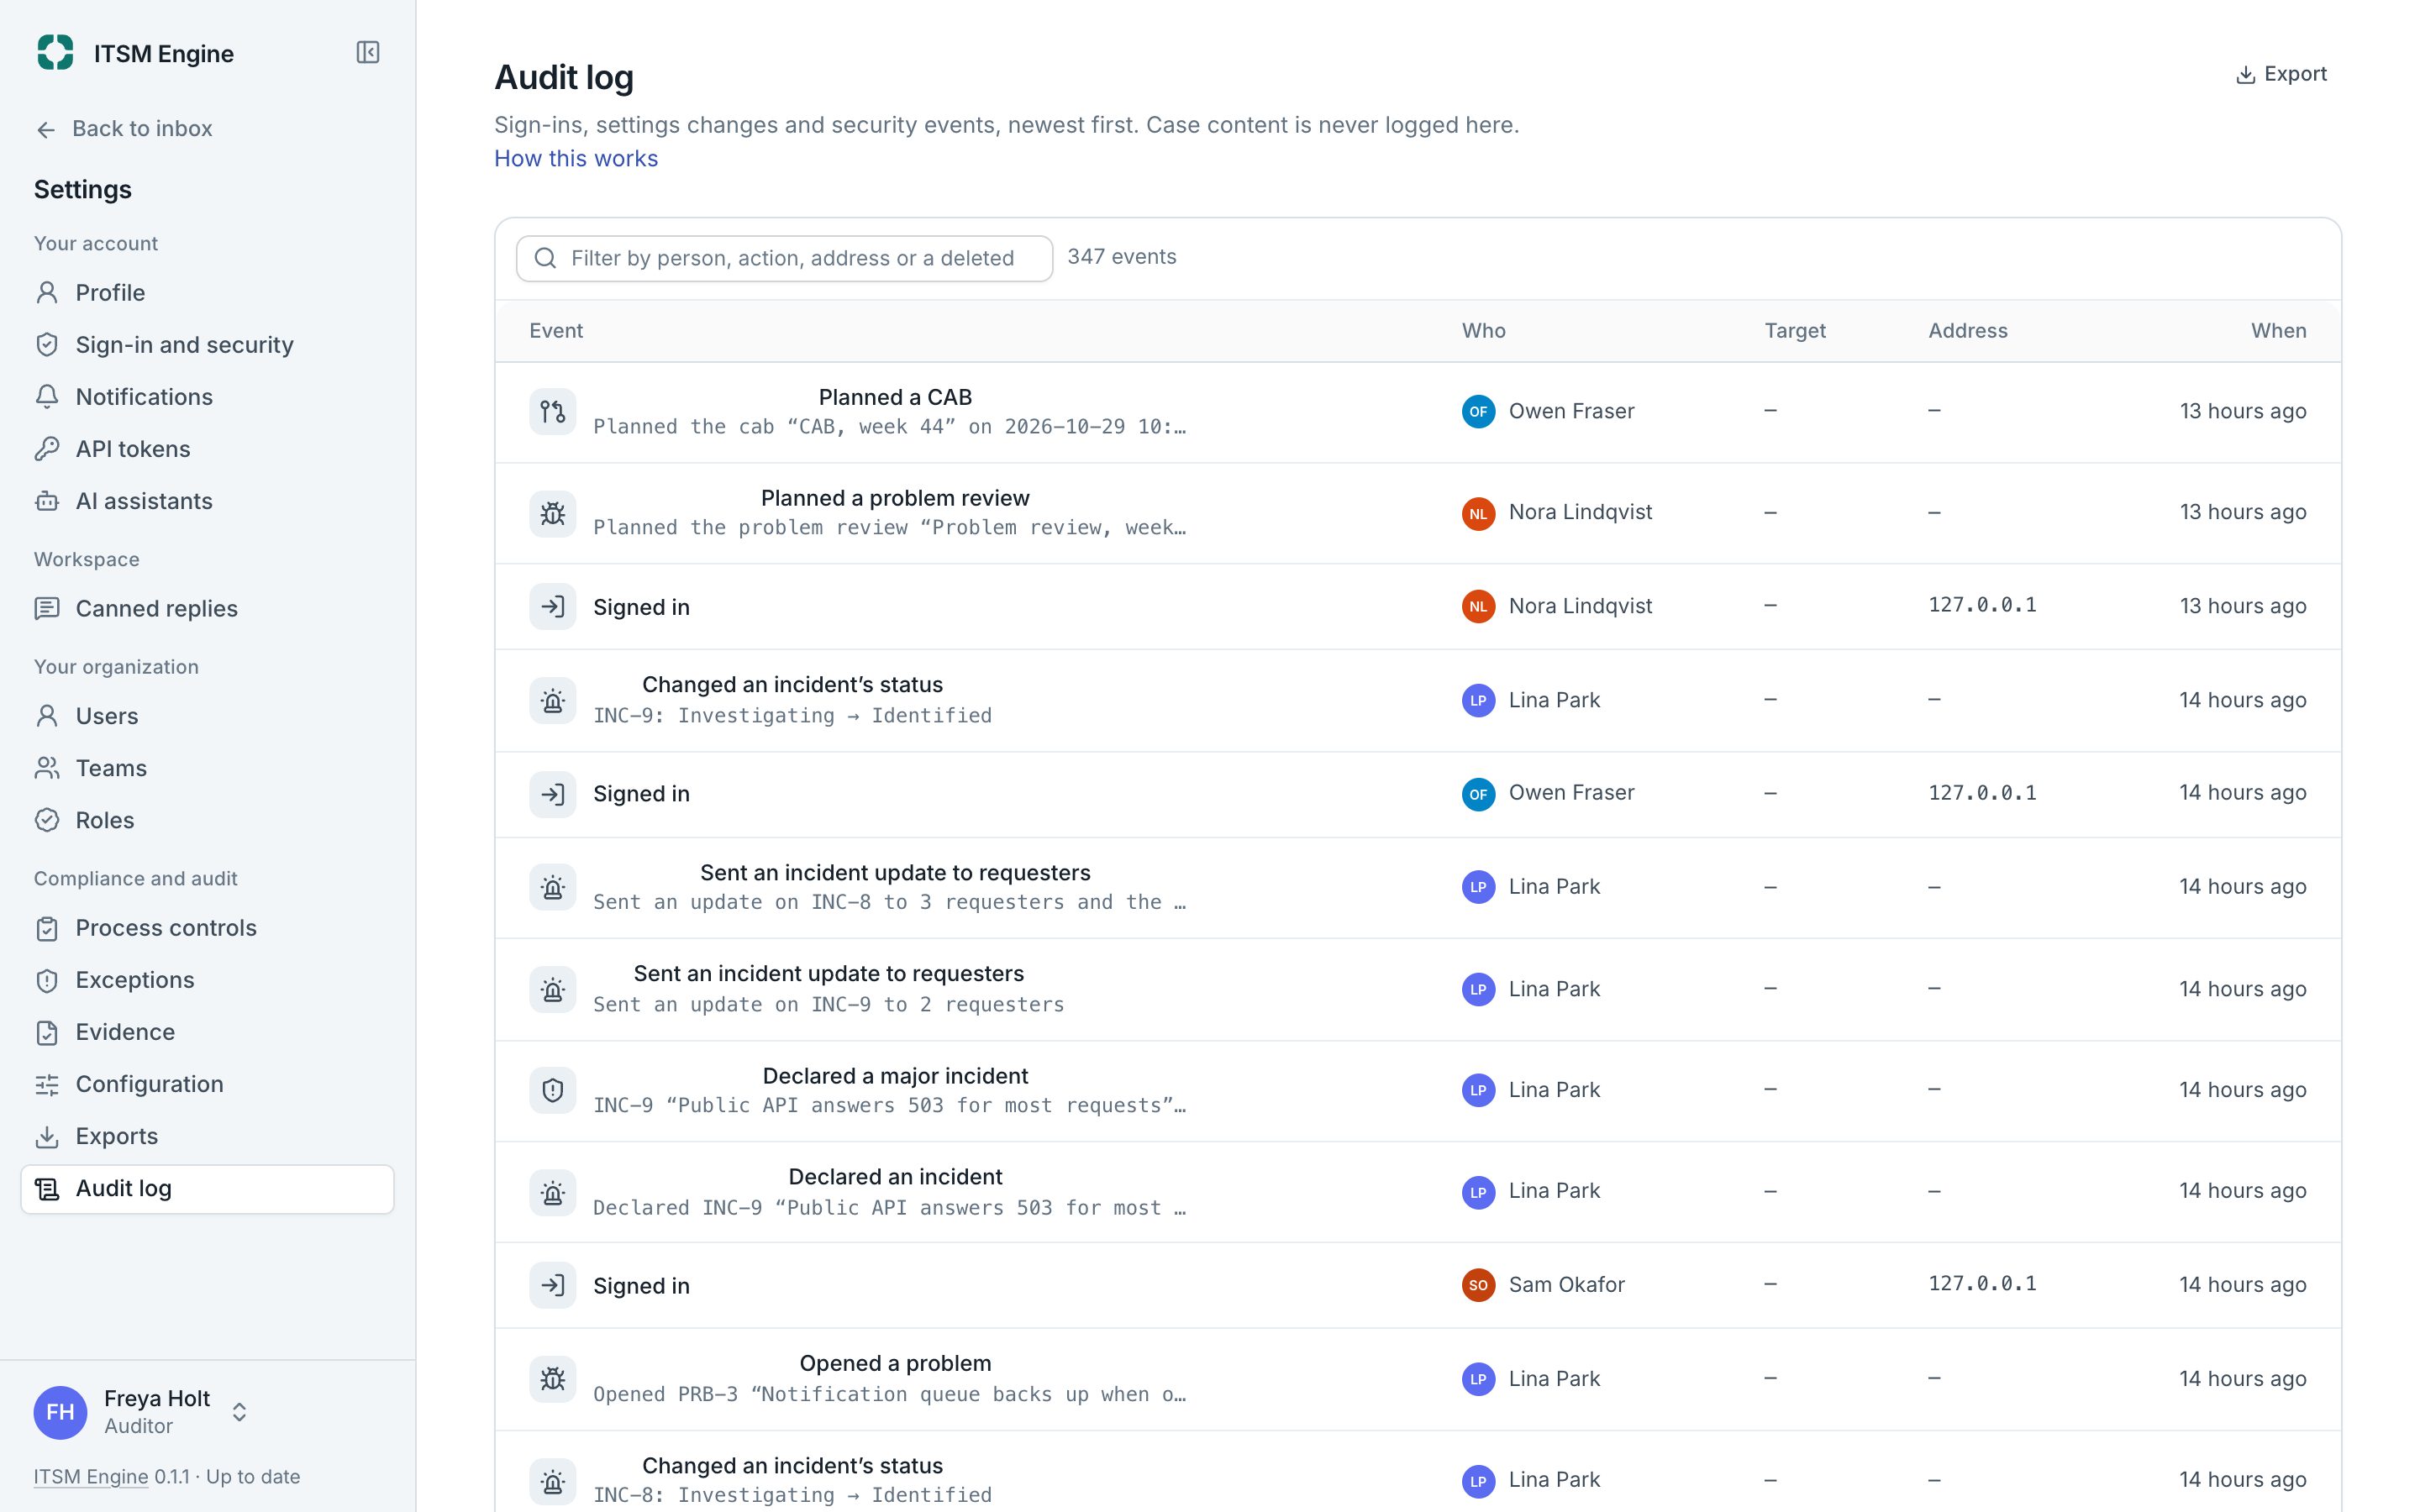
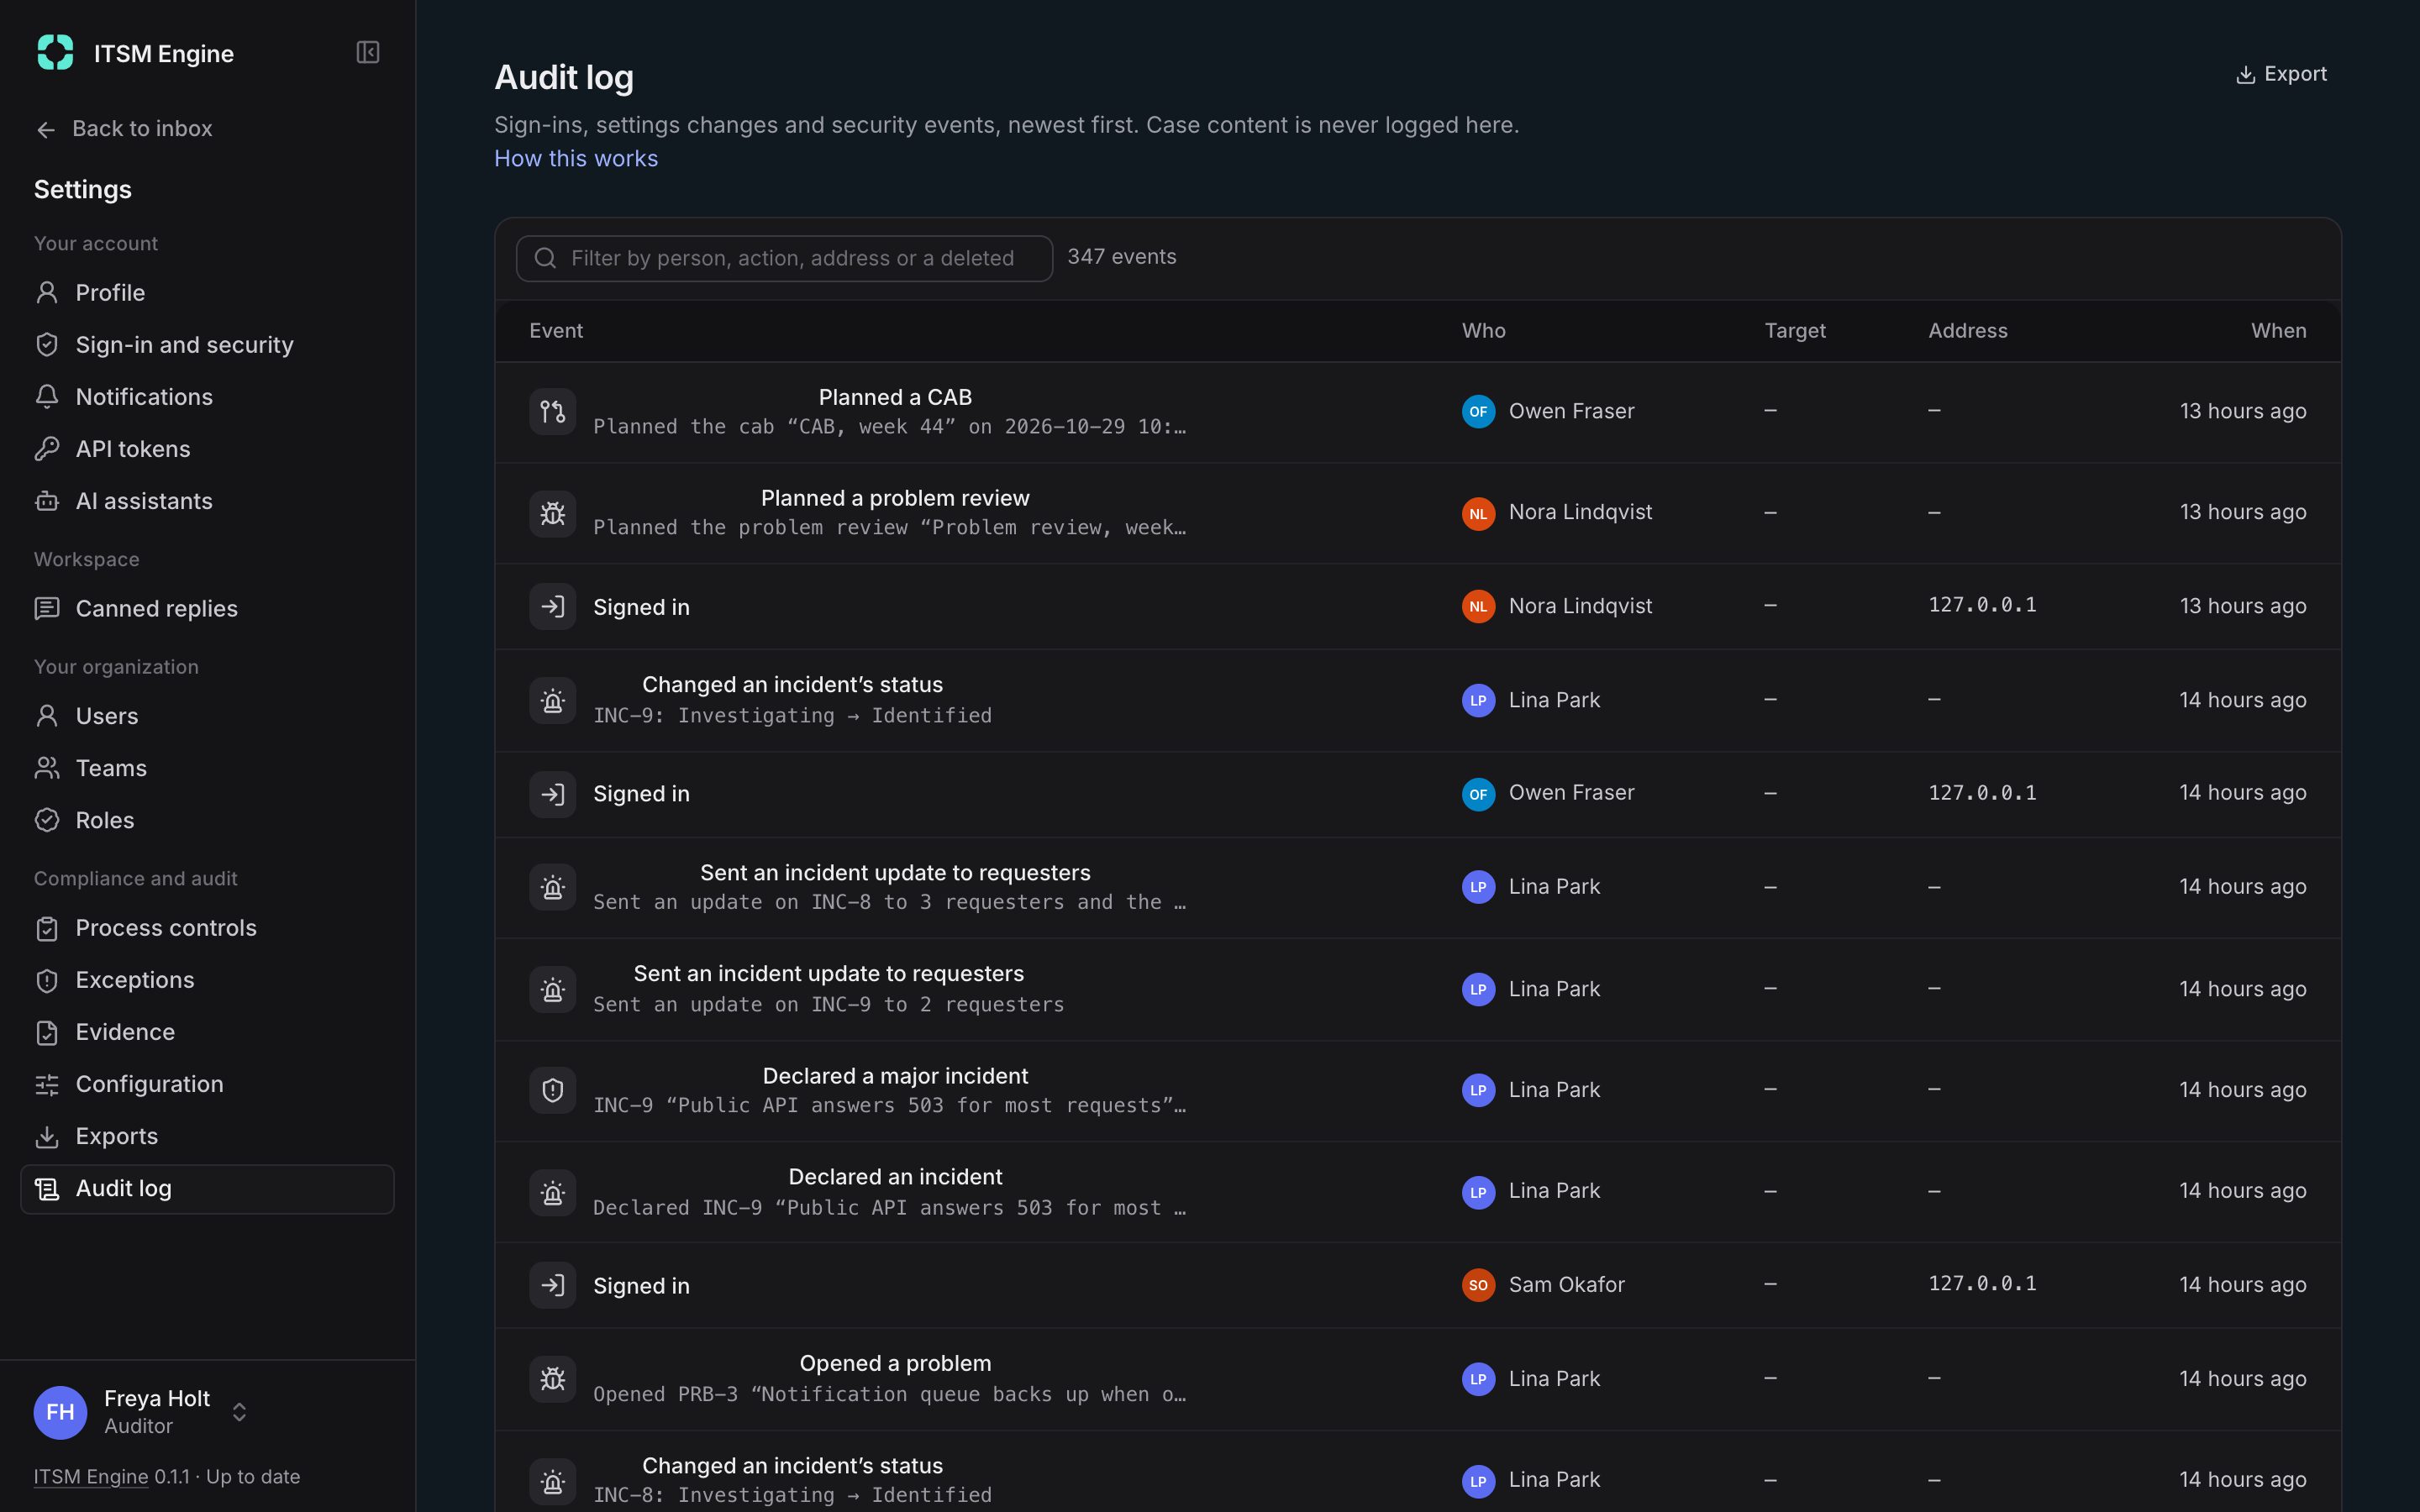
The audit log records the actions that matter to security and to an auditor, never the content of cases. Admins and auditors read it, filter it and export it with a checksum.
How it works
It records sign-ins and failed attempts, changes to users, roles, teams and units, settings such as service levels and automations with what they were before and after, deleted records with their reference, every write made with an API token and every tool an AI assistant used.
The Auditor role reads the log without admin rights, and its own reading is logged.
With the ITSM add-on, Access Reviews adds search, CSV export, retention per kind of entry and a hash-chain seal you can check at any time.
What it includes
Sign-ins
Successful and failed, with two-factor and passkeys.
Before and after
Settings changes with the old and the new value.
Deleted records
Who deleted which case, incident, problem or change, and when.
API and assistants
Every write by a token, every tool used by an AI assistant.
For auditors
The Auditor role reads it without admin rights.
Exported with a checksum
For the auditor’s working papers.